Single sign-on
SAML 2.0 and OpenID Connect with Microsoft Entra ID, Okta and other identity providers. Multi-factor authentication enforced by your identity provider. Local accounts with MFA where SSO is not used.
Security & Trust
Stream processes invoices, expenses and purchasing for organizations that answer to auditors. Identity, access, audit, encryption, data handling and AI use are designed to be explained, evidenced and reviewed.
Controls
What is in place today. Evidence for each control is available under NDA.
SAML 2.0 and OpenID Connect with Microsoft Entra ID, Okta and other identity providers. Multi-factor authentication enforced by your identity provider. Local accounts with MFA where SSO is not used.
Roles for AP processors, approvers, buyers, controllers, administrators and read-only auditors, scoped by entity, department and, where needed, vendor. Segregation of duties between submit, approve and post.
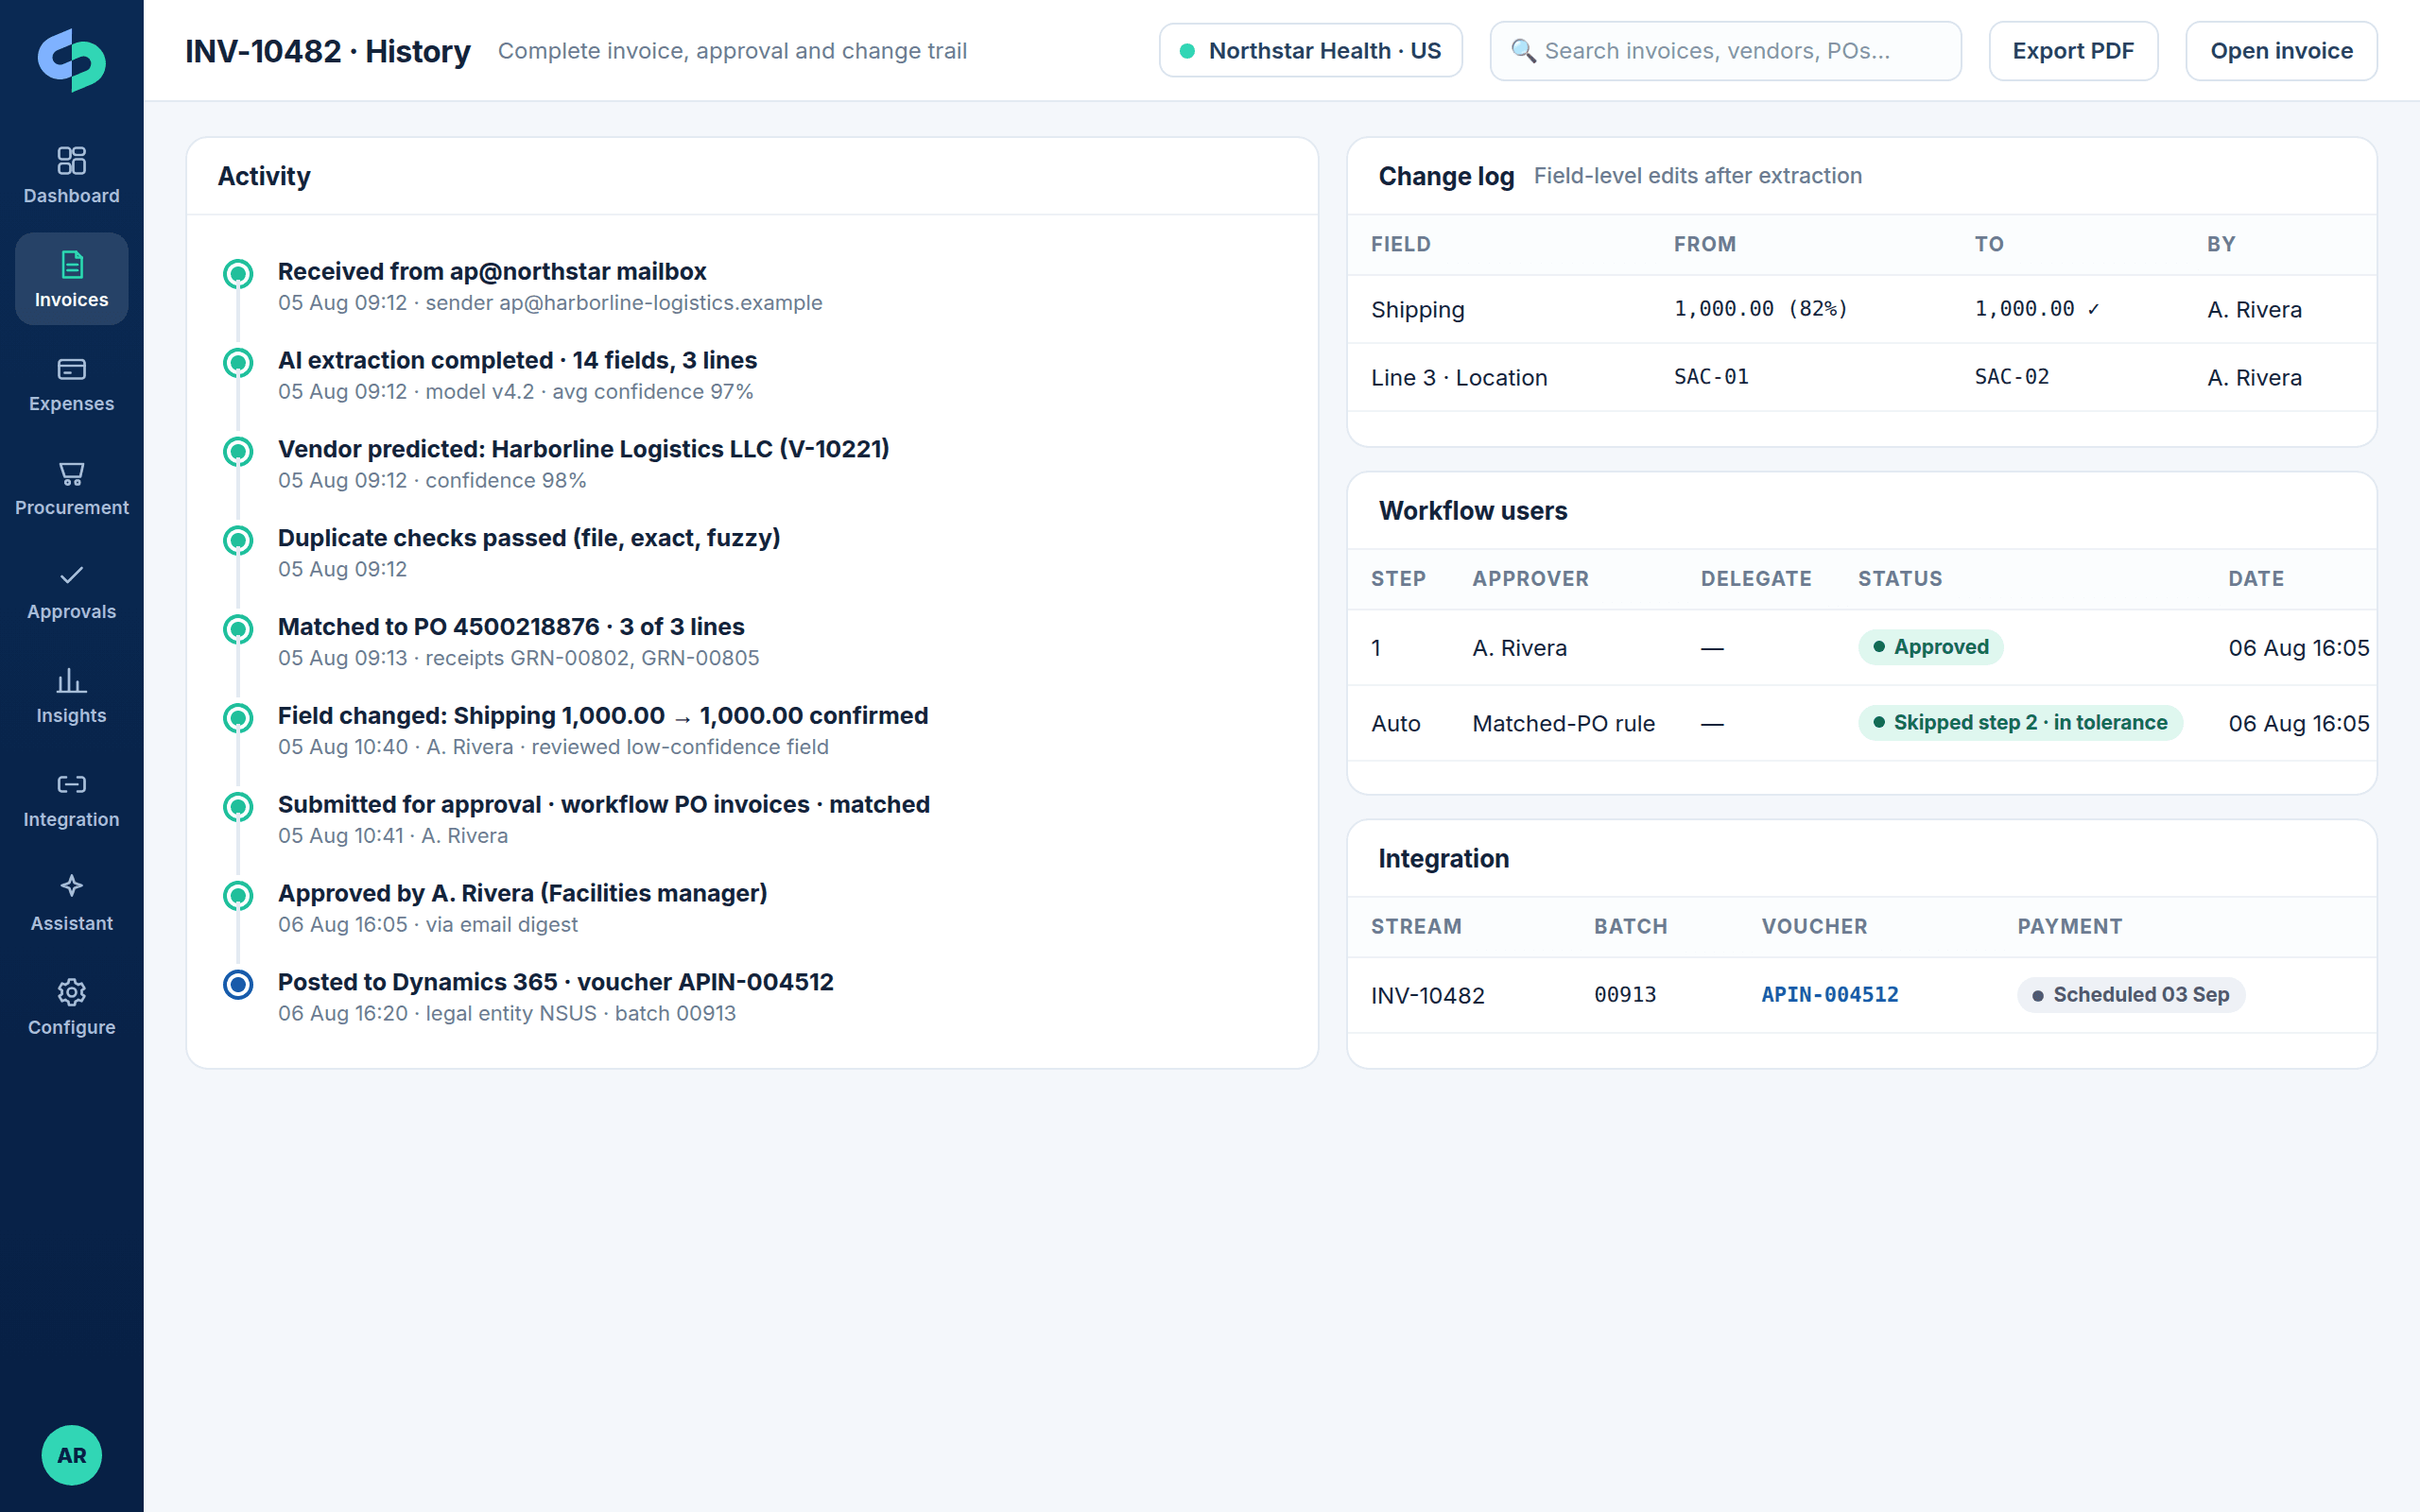
Every action on every invoice, expense report, PO, user and configuration change is logged with identity, timestamp and before-and-after values, exportable for audits.
Data encrypted in transit (TLS 1.2+) and at rest. Documents stored in customer-segregated storage with controlled access.
Cloud-hosted on Microsoft Azure with customer data logically isolated per tenant. Region selected at implementation.
Automated backups with retention, recovery objectives and testing cadence confirmed in your agreement.
Customer data is used only to deliver the service. Retention follows your policy; data is returned or deleted at contract end.
AI reads documents and suggests values for people to confirm. Your data is not used to train models for other customers. Predictions show confidence and reasons; low-confidence fields require human review.
Code review, dependency scanning, environment separation and change control on every release, with customer-visible release notes.
Attestations
We publish only what we can evidence. Attestation status is confirmed directly with the Skalable team and shared under NDA.
Current SOC 2 report status and scope are provided on request during evaluation.
Confirm with the teamIndependent application penetration tests with remediation tracking; summary letters available under NDA.
Summary on requestWe complete SIG, CAIQ and customer questionnaires and provide architecture and data-flow diagrams.
AvailableResponsible AI and customer data
AI in Stream reads documents and suggests values. People confirm, rules validate and the ERP remains the system of record.
Models are used for extraction, vendor identification, coding prediction and the Stream Assistant, nothing else.
Your documents and coding history improve your predictions; they are not used to train models for other customers.
Every prediction carries a confidence and a reason. Low-confidence fields require human confirmation.
Stream Assistant answers only with records the user is already allowed to see and cites the source.
Nothing posts to the ERP without the configured validation and approval path.
Sensitive fields can be masked in extraction and excluded from assistant responses by policy.
Questions
Current certification and attestation status, including SOC 2, is confirmed directly with the Skalable team and provided under NDA during evaluation. Ask for the security package on the contact page.
On Microsoft Azure, in a region agreed at implementation, with customer data logically isolated per tenant.
Yes. Access is scoped by role, entity and department, and can be narrowed further for sensitive vendors or projects.
A dedicated integration identity with least-privilege permissions, token-based authentication, encrypted transport and a full log of every call and posting.
A named contact and your questionnaire. We answer standard questionnaires (SIG, CAIQ, custom) and provide architecture and data-flow diagrams on request.
See also the privacy notice and terms.
Next step
Send your questionnaire with the demo request. Security reviews run in parallel with evaluation so they never delay go-live.